

What Is ASPM (Application Security Posture Management)?
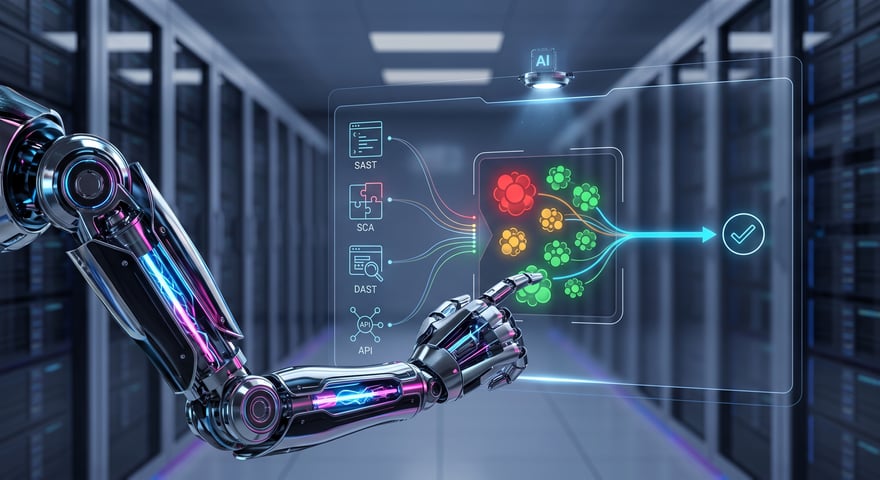
ASPM (Application Security Posture Management) is a category of appsec platforms with automation that unifies visibility, risk prioritization, and remediation across the entire application security landscape. Rather than treating security tools as isolated point solutions, ASPM consolidates findings from SAST, SCA, DAST, and API security testing into a single pane of glass, enabling security teams to understand their true risk posture and act on it efficiently. For organizations building AI-powered applications or operating at enterprise scale, ASPM represents the shift from reactive vulnerability management to proactive, automated security orchestration.
The rise of ASPM reflects a fundamental change in how modern security teams approach application protection. As development velocity accelerates and AI-native applications introduce new attack surfaces, the traditional model of siloed scanners and manual triage has become unsustainable. ASPM platforms address this by correlating data across the software development lifecycle, applying intelligent prioritization to surface the vulnerabilities that actually matter, and increasingly leveraging appsec automation to remediate issues without human intervention.
Why Traditional AppSec Tools Fall Short
Traditional application security tools were designed for a slower, more linear development process and cannot keep pace with modern DevSecOps workflows. These legacy approaches create fragmented visibility, overwhelming alert volumes, and friction between security and development teams that ultimately leaves organizations exposed.
The core problem is architectural. Point solutions like standalone SAST scanners or SCA tools operate in isolation, each generating its own findings without context about how those findings relate to the broader application environment. A vulnerability flagged by one tool may be unreachable in production, already mitigated by another control, or duplicated across multiple scanners—but traditional tools have no mechanism to correlate this information.
This fragmentation produces alert fatigue at scale. Security teams at mid-to-large enterprises routinely face thousands of findings per sprint, with no reliable way to distinguish critical risks from noise. The result is either paralysis—where teams cannot process the backlog—or dangerous shortcuts where genuine threats slip through because analysts are overwhelmed.
The DevSecOps gap compounds these challenges. Development teams shipping AI features weekly or daily cannot wait for manual security reviews that take days or weeks. When security becomes a bottleneck, it gets bypassed, and the era of automated, AI-driven remediation has made this tension even more acute. Organizations need security that moves at the speed of development, not against it.
Traditional tools also lack the contextual intelligence required for effective prioritization. Knowing that a dependency has a CVE is insufficient; security teams need to understand whether that dependency is actually deployed, whether the vulnerable function is called, and whether the application's architecture exposes it to exploitation. Without this context, every vulnerability looks equally urgent, which means none of them are treated with appropriate urgency.
Core Capabilities of ASPM Platforms
ASPM platforms deliver four foundational capabilities that transform application security from a fragmented, reactive discipline into a unified, proactive function: comprehensive visibility, intelligent prioritization, automated remediation, and continuous posture assessment.
Comprehensive visibility means aggregating findings from every security tool in the pipeline—SAST, SCA, DAST, container scanning, API security testing, and cloud security platforms—into a single normalized view. This consolidation eliminates the blind spots that occur when tools operate independently and provides security leaders with an accurate inventory of applications, dependencies, and associated risks across the organization.
Intelligent prioritization applies contextual analysis to separate critical vulnerabilities from noise. Leading ASPM platforms use reachability analysis to determine whether vulnerable code paths are actually exercised in production, business context to weight risks based on application criticality, and exploit intelligence to identify vulnerabilities actively targeted in the wild. This approach can reduce actionable findings by an order of magnitude compared to raw scanner output.
Automated remediation extends beyond alerting to actually fixing issues. Modern ASPM platforms can generate patches, open pull requests, and in some cases deploy fixes automatically when confidence thresholds are met. Vulnerability triage automation has become a foundational workflow within ASPM, enabling security teams to handle volumes that would be impossible manually while maintaining accuracy.
Continuous posture assessment provides ongoing measurement of security health rather than point-in-time snapshots. ASPM platforms track metrics like mean-time-to-remediation, vulnerability density trends, and coverage gaps across the application portfolio, giving security leaders the data they need to demonstrate ROI and identify systemic weaknesses before they become incidents.
These capabilities work together to create a security orchestration automation and response software layer purpose-built for application security, distinct from the infrastructure-focused SOAR platforms that preceded it.
How ASPM Enables AppSec Automation Across the SDLC
ASPM enables appsec automation by embedding security controls directly into development workflows rather than bolting them on after the fact. This integration spans the entire software development lifecycle, from code commit through production deployment.
At the code commit stage, ASPM platforms trigger security testing automation tools automatically when developers push changes. Rather than running full scans that take hours, intelligent ASPM implementations perform incremental analysis focused on changed code paths, returning results in minutes. This speed is essential for maintaining developer productivity while ensuring security coverage.
During the build phase, ASPM orchestrates multiple scanning modalities—SAST for source code analysis, SCA for dependency vulnerabilities, and secrets detection for credential exposure—correlating their findings in real time. When a vulnerability is detected, the platform can block the build, notify the developer, and in many cases suggest or automatically apply a fix before the code ever reaches a shared branch.
The deployment pipeline represents another critical automation point. ASPM platforms integrate with CI/CD systems to enforce security gates based on policy—preventing deployments that introduce critical vulnerabilities or violate compliance requirements. These gates can be configured with nuance, allowing exceptions for low-risk changes while maintaining strict controls for sensitive applications.
Post-deployment, ASPM continues monitoring through integration with runtime security tools and cloud security automation systems. Vulnerabilities discovered in production can be traced back to their source, and the platform can automatically prioritize remediation based on actual exposure rather than theoretical risk.
This end-to-end automation represents the evolution toward agentic appsec automation platforms that can operate with increasing autonomy, handling routine security tasks without human intervention while escalating complex decisions to analysts.
ASPM for AI-Native Applications and Compliance
AI-native applications introduce security challenges that traditional AppSec approaches were never designed to address, making ASPM particularly valuable for organizations deploying machine learning models and generative AI features. These applications expand the attack surface in ways that require new forms of visibility and control.
AI/ML pipelines involve data flows, model artifacts, and inference endpoints that exist outside conventional application boundaries. ASPM platforms designed for AI-native environments can inventory these components, track their dependencies, and identify vulnerabilities specific to machine learning infrastructure—such as model poisoning risks, training data exposure, or prompt injection vulnerabilities in LLM-powered features.
Compliance requirements for AI applications are evolving rapidly. Frameworks like NIST AI RMF establish governance expectations that overlap with but extend beyond traditional application security controls. ASPM platforms help compliance-driven buyers meet these requirements by providing audit trails, policy enforcement, and continuous monitoring that demonstrate due diligence to regulators and auditors.
For organizations in regulated industries—finance, healthcare, government—the compliance automation capabilities of ASPM are often the primary driver of adoption. Security content automation protocol software integration enables standardized vulnerability reporting, while built-in policy engines can map findings to specific regulatory requirements and generate audit-ready documentation automatically.
The governance dimension is equally important. Agentic appsec tools require stability and governance frameworks to ensure that automated remediation actions align with organizational policies and do not introduce unintended consequences. ASPM platforms provide the control plane for managing this automation safely.
Enterprise-scale deployments face additional considerations around multi-cloud environments, distributed development teams, and complex application portfolios. AI appsec platforms designed for enterprises address these requirements with features like role-based access control, tenant isolation, and integration with enterprise identity providers.
Comparing Top AppSec Platforms with Automation
Evaluating appsec companies offering ASPM capabilities requires understanding the key differentiators that separate effective platforms from those that simply aggregate scanner output without adding intelligence.
Scanning breadth and depth determines whether a platform can serve as a true consolidation point. The most capable ASPM platforms support SAST, SCA, DAST, container security, infrastructure-as-code scanning, and API security platforms through native capabilities or deep integrations. Platforms that only address a subset of these modalities leave gaps that require additional point solutions.
Prioritization intelligence varies significantly across vendors. Basic platforms rank by CVSS score alone, which produces poor signal-to-noise ratios. Advanced platforms incorporate reachability analysis, exploit prediction, business context, and environmental factors to surface the vulnerabilities that represent actual risk. This capability directly impacts security team productivity and remediation effectiveness.
Automation capabilities range from simple alerting to fully autonomous remediation. Some platforms stop at creating tickets; others generate pull requests with suggested fixes; the most advanced can deploy patches automatically when confidence thresholds are met. The right level of automation depends on organizational risk tolerance and maturity.
CI/CD integration depth affects how seamlessly security fits into development workflows. Platforms with native integrations for major CI/CD systems, IDE plugins for developer feedback, and API-first architectures enable the frictionless experience that DevSecOps practitioners require.
Cloud security platforms integration has become essential as applications increasingly run on cloud infrastructure. ASPM platforms that correlate application vulnerabilities with cloud misconfigurations provide more complete risk visibility than those that treat these domains separately.
For a detailed comparison of leading vendors in this space, including evaluation criteria and use case recommendations, see our guide to the best AI appsec platforms and vendors.
Get Started with AI-Powered ASPM
Adopting ASPM requires a structured approach that balances immediate security improvements with long-term platform consolidation goals. Organizations typically succeed by starting with high-value use cases and expanding coverage incrementally.
Begin by inventorying your current application security tooling and identifying the gaps and overlaps that ASPM can address. Most organizations discover they have multiple scanners producing redundant findings, manual triage processes that cannot scale, and limited visibility into their true application portfolio. Documenting these pain points establishes the baseline for measuring ASPM impact.
Prioritize integration with your CI/CD pipeline as the first implementation milestone. This integration delivers immediate value by automating security testing for new code while establishing the foundation for more advanced automation. Focus on a single high-priority application or team initially, then expand based on lessons learned.
Define clear success metrics before deployment. Mean-time-to-remediation, false positive rates, and vulnerability escape rates provide objective measures of ASPM effectiveness. Security leaders need these metrics to demonstrate ROI to executive leadership and justify continued investment in automation in cybersecurity.
Evaluate platforms based on your specific requirements rather than generic feature checklists. Organizations with significant AI/ML deployments need platforms that understand those workloads. Compliance-driven buyers should prioritize audit automation and policy enforcement. DevSecOps teams should weight developer experience and CI/CD integration heavily.
For practical guidance on selecting the right platform for your organization, the guide to choosing the best AI appsec platform for modern security teams provides a decision framework tailored to 2026 requirements. Teams ready to evaluate specific solutions should consult the agentic appsec tools buyer's guide for detailed vendor assessments and implementation considerations.
Frequently Asked Questions
What is an AppSec platform with automation?
An AppSec platform with automation is a security solution that combines application security testing capabilities with automated workflows for vulnerability detection, prioritization, and remediation. These platforms integrate SAST, SCA, DAST, and other scanning technologies into a unified system that can trigger scans automatically, correlate findings across tools, and in many cases fix vulnerabilities without manual intervention. The automation extends across the SDLC, from code commit through production deployment.
How does ASPM differ from traditional application security tools?
ASPM differs from traditional application security tools by providing unified visibility and orchestration rather than isolated scanning. Traditional tools like standalone SAST or SCA scanners operate independently, each producing separate findings without context about the broader application environment. ASPM consolidates these findings, applies intelligent prioritization based on reachability and business context, and automates remediation workflows. This distinction parallels the broader difference between infosec vs appsec approaches—ASPM brings the posture management philosophy from infrastructure security into the application domain.
What capabilities should I look for in an appsec platform with automation?
Look for comprehensive scanning coverage across SAST, SCA, DAST, and API security; intelligent prioritization using reachability analysis and exploit intelligence; native CI/CD integration that fits your existing pipeline; automated remediation capabilities including patch generation and pull request creation; and continuous posture monitoring with audit-ready reporting. The platform should reduce false positives significantly compared to raw scanner output and provide clear metrics for measuring security program effectiveness.
How does AppSec automation integrate with CI/CD pipelines?
AppSec automation integrates with CI/CD pipelines through native plugins, webhooks, or API calls that trigger security scans at defined stages—typically on code commit, pull request, and pre-deployment. The platform analyzes changes incrementally to return results quickly, enforces security gates that can block deployments violating policy, and provides developer feedback directly in the tools they already use. Advanced integrations can automatically apply fixes and re-run validation without human intervention.
How do automated AppSec platforms reduce false positives and alert fatigue?
Automated AppSec platforms reduce false positives through reachability analysis that determines whether vulnerable code paths are actually executed, deduplication across multiple scanners, contextual risk scoring that considers deployment environment and exploit availability, and machine learning models trained on historical triage decisions. These techniques can reduce actionable findings by 80-90% compared to raw scanner output, enabling security teams to focus on vulnerabilities that represent genuine risk.
Can a single AppSec platform automate SAST, SCA, and API security testing?
Yes, modern ASPM platforms can automate SAST, SCA, and API security testing within a single solution, either through native scanning engines or deep integrations with specialized tools. This consolidation eliminates the need to manage multiple point solutions, correlates findings across testing modalities, and provides unified policy enforcement. Organizations should verify that a platform's coverage matches their technology stack and that integrations provide the depth required for accurate correlation.
How do appsec automation tools support compliance and audit requirements?
Appsec automation tools support compliance by providing continuous monitoring against policy requirements, generating audit trails for all security activities, mapping vulnerabilities to specific regulatory frameworks, and producing documentation automatically. Platforms with security content automation protocol software integration enable standardized reporting formats. For AI applications specifically, ASPM platforms can track compliance with emerging frameworks like NIST AI RMF and provide evidence of security controls for auditors and regulators.
Subscribe to Amplify Weekly Blog Roundup
Subscribe Here!
See What Experts Are Saying
BOOK A DEMO
Jeremiah Grossman
Founder | Investor | Advisor
Saeed Abu-Nimeh
CEO and Founder @ SecLytics
Kathy Wang
CISO | Investor | Advisor

Alex Lanstein
Chief Evangelist @ StrikeReadyFrequently
Asked Questions
What is vulnerability management, and why is it important?
Why is vulnerability management important?
What makes vulnerability management extremely challenging in today’s high-growth environment?
How can Amplify help me with vulnerability management?
What technology does the Amplify platform integrate with?
Have a
Questions?
Contact Us
Ready to
Get started?
Book A GUIDED DEMO
