

What is Auto Remediation in AppSec? Definition and How It Works
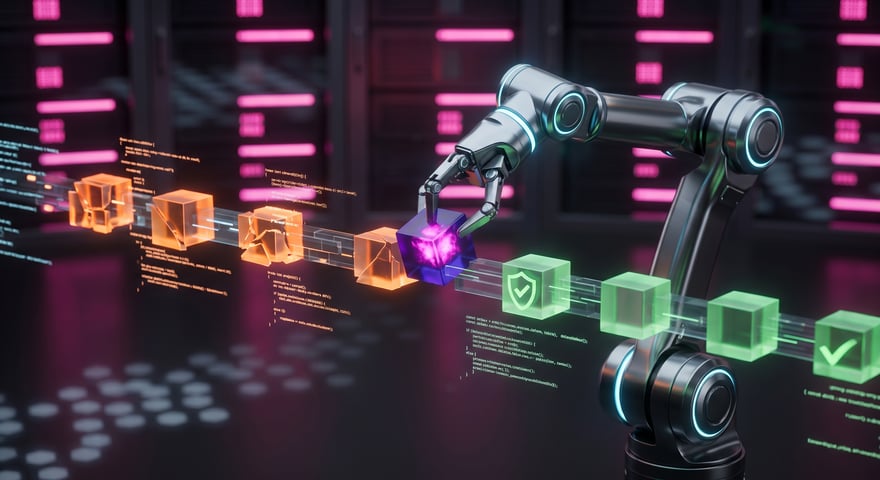
Auto remediation in application security (AppSec) is the automated process that detects, triages, and fixes security vulnerabilities in code, dependencies, or infrastructure configurations without requiring manual developer intervention for every finding. It combines vulnerability scanners (SAST, DAST, SCA) with automated fix-generation engines that produce patches, dependency upgrades, or configuration changes, then submit those fixes as pull requests or direct commits into the development workflow. The goal is to reduce mean time to remediation (MTTR) from days or weeks to minutes or hours.
Why does auto remediation matter in AppSec?
Security teams face a persistent volume problem. A typical enterprise application portfolio generates thousands of vulnerability findings per quarter across static analysis, software composition analysis, container scanning, and cloud configuration audits. Manual remediation creates bottlenecks:
Developer fatigue: engineers context-switch away from feature work to triage findings they may not fully understand.
Backlog growth: findings accumulate faster than teams can fix them, creating a growing risk surface.
Slow MTTR: the Veracode State of Software Security report consistently shows that median time to fix known vulnerabilities stretches beyond 200 days for many organizations.
Inconsistent prioritization: without automation, severity-based prioritization often stalls on organizational friction rather than technical complexity.
Auto remediation removes the manual steps between detection and fix, reducing MTTR and backlog.
How does auto remediation work?
The auto remediation pipeline typically follows a five-stage process:
Stage 1: Vulnerability detection
Scanners identify findings. These can be:
- SAST tools flagging injection flaws, hardcoded secrets, or insecure cryptographic usage in source code
- SCA tools identifying known CVEs in open-source dependencies
- DAST tools discovering runtime vulnerabilities like XSS or authentication bypass
- IaC scanners detecting misconfigured Terraform, CloudFormation, or Kubernetes manifests
Stage 2: Triage and deduplication
Raw scanner output is noisy. Auto remediation systems apply deduplication, reachability analysis, and contextual risk scoring to filter actionable findings from false positives. Key factors include:
- Whether the vulnerable code path is actually reachable at runtime
- Whether the affected dependency is in a production build or only a dev/test scope
- The exploitability and severity (CVSS, EPSS scores)
- Whether a fix is actually available
Stage 3: Fix generation
Fix generation is the core differentiator. Fix generation approaches vary by vulnerability type:
|
Vulnerability type |
Fix approach |
Example |
|
Outdated dependency with known CVE |
Version bump |
Upgrade lodash from 4.17.20 to 4.17.21 |
|
SQL injection in source code |
Code patch |
Replace string concatenation with parameterized queries |
|
Hardcoded secret |
Secret removal and vault reference |
Replace inline API key with environment variable lookup |
|
IaC misconfiguration |
Config patch |
Set PublicAccessBlockConfiguration to true on S3 bucket |
|
Insecure TLS configuration |
Config update |
Remove TLS 1.0/1.1 from allowed protocols |
Dependency upgrades are the most mature and reliable category for auto remediation. Source code patches require more sophisticated analysis, often using AST (abstract syntax tree) transformations or large language models; these carry higher risk of introducing functional regressions.
Stage 4: Validation
Before submitting a fix, the system validates it:
- Build verification, does the patched code still compile?
- Test suite execution, do existing unit and integration tests pass?
- Security re-scan, does the fix actually resolve the original finding without introducing new ones?
- Compatibility checks, for dependency upgrades, are there breaking API changes?
Fixes that fail validation are flagged for manual review rather than merged automatically.
Stage 5: Delivery
Validated fixes are integrated through the existing developer workflow:
- Pull request or merge request, the most common delivery mechanism. Developers review and merge.
- Auto-merge, for low-risk, high-confidence fixes such as patch-level dependency bumps with passing tests, some teams enable automatic merging.
- Ticket creation, when a fix cannot be fully automated, a detailed ticket with remediation guidance is created in Jira, GitHub Issues, or similar systems.
What types of vulnerabilities can be auto remediated?
Not all vulnerabilities are equally amenable to automated fixing. A practical breakdown:
High automation confidence:
- Known CVEs in direct dependencies (version bumps)
- Transitive dependency vulnerabilities (lock file updates)
- IaC misconfigurations with deterministic fixes
- Secret detection and rotation
- Security header misconfigurations
Medium automation confidence:
- Common code-level patterns (SQL injection, path traversal) with well-understood fix templates
- Dockerfile best practice violations
- Deprecated API usage
Low automation confidence (human review essential):
- Business logic vulnerabilities
- Authentication and authorization design flaws
- Complex multi-file code refactors
- Vulnerabilities requiring architectural changes
What are the risks and limitations?
Auto remediation is not a silver bullet. Practitioners should be aware of several concrete risks:
Breaking changes: a dependency upgrade that passes unit tests may still break production behavior if test coverage is low.
Fix correctness: LLM-generated code patches can introduce subtle bugs. AST-based transformations are more deterministic but less flexible.
False confidence: teams may assume a vulnerability is resolved because a PR was merged, without verifying the fix addresses the root cause.
Supply chain risk: automatically upgrading to a new dependency version assumes that version is trustworthy. Typosquatting and dependency confusion attacks exploit exactly this assumption.
Scope creep: auto-merging fixes without review erodes developer ownership of code quality and security posture.
How do you mitigate these risks?
- Require human review for any fix that modifies application logic, not just dependency manifests
- Enforce minimum test coverage thresholds before enabling auto-merge
- Pin auto-merge eligibility to patch-level bumps only, not minor or major version changes
- Integrate with provenance verification tools (Sigstore, SLSA) for dependency upgrades
- Maintain an audit trail of all automated changes
How does auto remediation fit into the SDLC?
Auto remediation is most effective when embedded directly into CI/CD pipelines rather than bolted on as a periodic batch process.
Shift-left integration points:
- Pre-commit hooks catch secrets and simple misconfigurations before code enters the repository
- PR-time scanning triggers scans on every pull request and can provide fix suggestions as PR comments or companion PRs
- CI pipeline gates block merges when critical or high findings exist and no remediation is available
- Scheduled dependency scans run SCA on a daily or weekly cadence to catch newly disclosed CVEs in existing dependencies
Post-deployment integration points:
- Runtime monitoring detects vulnerabilities exploited in production and can trigger emergency patches
- Drift detection identifies IaC configurations that have drifted from their remediated state
What should you look for in an auto remediation solution?
When evaluating tools or platforms, focus on these capabilities:
- Scanner coverage: does it ingest findings from the scanners you already use, or does it require its own?
- Fix accuracy: what percentage of generated fixes pass validation without manual modification?
- Language and framework support: does it support your primary tech stack?
- Merge policy controls: can you define granular rules for what gets auto-merged versus what requires review?
- Audit and compliance: does it produce evidence artifacts for SOC 2, FedRAMP, or other compliance frameworks?
- Developer experience: are fixes provided where developers already work (GitHub, GitLab, Bitbucket, Azure DevOps)?
- Reachability analysis: can it distinguish between a vulnerable dependency that is actually invoked and one that is present but unused?
Prioritize platforms that ingest existing scanner output and submit fixes into developer workflows.
How is auto remediation different from auto triage?
|
Capability |
What it does |
Outcome |
|
Auto triage |
Prioritizes and filters findings based on risk context |
Reduces noise and tells you what to fix first |
|
Auto remediation |
Generates and delivers the actual fix |
Reduces MTTR and performs the fix |
A mature AppSec program uses both: auto triage to focus attention and auto remediation to accelerate resolution.
Where is auto remediation heading?
Several trends are shaping the next generation of auto remediation:
LLM-assisted patching, large language models are being used to generate code-level fixes beyond simple template matching. Accuracy is improving but still requires guardrails.
Runtime-informed prioritization, combining static findings with runtime observability data (which functions are actually called, which endpoints are exposed) to remediate only what matters.
Policy-as-code remediation, defining organizational security policies declaratively and having remediation engines enforce them automatically across all repositories.
Continuous compliance, auto remediation tied to compliance controls that produce audit-ready evidence showing a vulnerability was detected, fixed, validated, and deployed within a defined SLA.
FAQ
Is auto remediation safe to use in production codebases?
Yes, when scoped correctly. High-confidence fixes, such as patch-level dependency bumps, IaC misconfigurations with deterministic fixes, and secret rotation, carry low regression risk and are safe candidates for auto-merge with passing tests. Code-level patches and anything touching business logic should route through human review rather than auto-merge.
Does auto remediation replace the need for a security team?
No. Auto remediation removes repetitive, low-judgment work (version bumps, config patches, ticket creation) so security engineers can spend time on architectural risk, authentication design, and findings that need human context. It's a force multiplier, not a replacement.
What's the difference between auto remediation and a dependency bot like Dependabot or Renovate?
Dependency bots focus narrowly on version bumps for known CVEs. Full auto remediation platforms cover a wider vulnerability surface, including SAST findings, IaC misconfigurations, and hardcoded secrets, and typically add triage, reachability analysis, and validation steps before a fix ever reaches a PR.
Can auto remediation fix zero-day vulnerabilities?
Only indirectly. Auto remediation depends on a scanner (SAST/DAST/SCA) surfacing a finding and, for dependency issues, a patched version already existing upstream. It shortens the time between disclosure and fix, but it doesn't discover unknown vulnerabilities on its own.
How do I know if a fix generated automatically is trustworthy?
Look for validation before delivery: build verification, test suite execution, a security re-scan confirming the finding is actually resolved, and compatibility checks for breaking changes. Fixes that fail any of these should be flagged for manual review, not merged automatically.
Will auto remediation break my build?
It can, if test coverage is thin. A dependency upgrade that passes a weak test suite may still change runtime behavior. Mitigate this by pinning auto-merge to patch-level bumps only and enforcing a minimum coverage threshold before auto-merge is enabled for a given repo.
What compliance frameworks does auto remediation support?
Mature platforms generate audit-ready evidence, including detection timestamp, fix applied, validation results, and deployment confirmation, mapped to frameworks like SOC 2 and FedRAMP. This turns remediation SLAs into something you can prove, not just claim.
Conclusion
Vulnerability backlogs don't grow because security teams lack findings; they grow because there's no scalable path from finding to fix. Auto remediation closes that gap: it turns thousands of scanner alerts into validated pull requests, without asking every engineer to become a security expert or every security engineer to review every dependency bump by hand.
The programs that get the most value from auto remediation treat it as infrastructure, not a one-time tool rollout, with tuned merge policies, enforced test coverage, and an audit trail baked into CI/CD from day one.
Ready to cut your MTTR from months to hours? See how Amplify Security plugs into your existing scanners and delivers validated, review-ready fixes directly into your developer workflow. Book a demo or start a free trial to see it on your own repos.
Subscribe to Amplify Weekly Blog Roundup
Subscribe Here!
See What Experts Are Saying
BOOK A DEMO
Jeremiah Grossman
Founder | Investor | Advisor
Saeed Abu-Nimeh
CEO and Founder @ SecLytics
Kathy Wang
CISO | Investor | Advisor

Alex Lanstein
Chief Evangelist @ StrikeReadyFrequently
Asked Questions
What is vulnerability management, and why is it important?
Why is vulnerability management important?
What makes vulnerability management extremely challenging in today’s high-growth environment?
How can Amplify help me with vulnerability management?
What technology does the Amplify platform integrate with?
Have a
Questions?
Contact Us
Ready to
Get started?
Book A GUIDED DEMO
