

The AppSec Guide to Buying Automated SAST Triage Tools
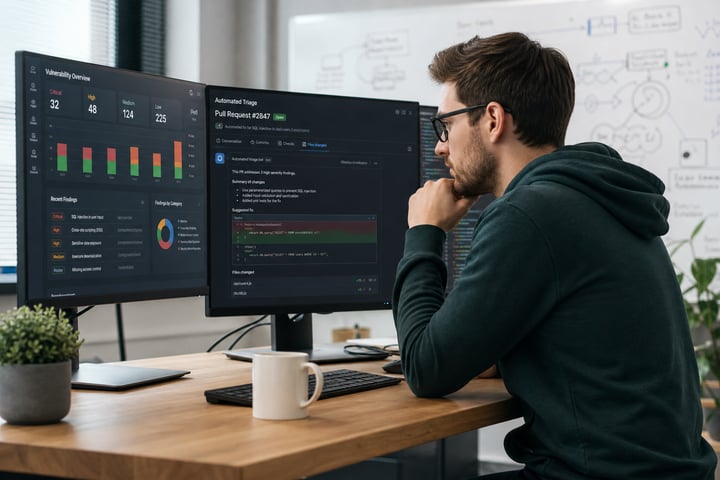
Security teams are drowning in a sea of vulnerabilities. Legacy Static Application Security Testing tools are excellent at finding potential flaws. They are notoriously terrible at providing context. The result is a backlog of thousands of alerts, crippling developer velocity and burning out security engineers who spend their days manually verifying false positives.
Related resources:
Explore the agentic AI cybersecurity platform
Compare agentic security harnesses
In the last two years, software engineers acquired a new gear. Tools like Cursor and Claude Code collapsed the gap between having an idea and having working code. Pull request volume is up, features ship in days instead of weeks, and the total volume of code keeps multiplying. Now ask the security engineer on that same team how their workflow has changed. Mostly, it hasn't. Devs got agentic engineering harnesses. Security got more alerts and a faster-moving target.
When you decide to buy automated SAST triage tools, you are not just purchasing another scanner. You are investing in a workflow optimization platform designed to bridge the gap between finding a vulnerability and actually fixing it. This guide outlines exactly what technical capabilities, integration points, and operational metrics you must evaluate before selecting a solution for your application security program.
The Core Problem with Legacy SAST Workflows
The fundamental architecture of early SAST tools relied on rigid pattern matching and data flow analysis without an understanding of business logic or runtime context. This approach guarantees a high false positive rate. Security teams respond by tuning rulesets, which takes months of dedicated effort and often leads to false negatives where critical vulnerabilities slip through the cracks.
The manual triage workflow is unsustainable for modern engineering teams. When a scanner flags a cross-site scripting vulnerability, a security engineer must locate the specific repository, trace the data flow from source to sink, determine if a sanitization library is already handling the input, and check if the vulnerable code is even reachable in production. This process takes anywhere from fifteen minutes to several hours per alert.
When an organization scales to hundreds of repositories and multiple daily deployments, manual triage becomes a mathematical impossibility. The bottleneck shifts from discovering vulnerabilities to verifying them, forcing security leaders to choose between blocking deployments and ignoring alerts. Neither choice is acceptable for a mature security program.
Your business also has security requirements that generic scanners were never built to understand. You might have customer data that's only allowed in the production database, encrypted in specific ways. You might have actions that need audit logging for compliance. A generic SAST tool sees the code, but you see the business it serves, and your business doesn't have an average risk model. When you buy automated SAST triage tools, you're buying the ability to inject your specific business logic into the vulnerability management process.
Defining Automated SAST Triage
Automated triage fundamentally changes how security teams interact with scan results. Instead of presenting a raw list of findings, an automated triage platform ingests the alerts from your existing scanners and applies secondary layers of analysis. The goal is to filter out the noise, prioritize the critical issues, and present developers with verified, actionable tasks.
A modern triage tool utilizes advanced contextual analysis. It understands the frameworks your developers are using, knows the difference between test code and production code, and evaluates the exploitability of a flaw based on the surrounding architecture. By automating the verification steps a human engineer would normally perform, these platforms reduce alert volume by massive margins, in practice, teams that implement reachability-based filtering can reduce their backlog by up to ninety percent, focusing entirely on issues that actually matter.
The best tools in this category go beyond simple filtering. They identify the exact line of code requiring modification and generate the necessary fix. This transforms the security team from a blocker into an enabler, providing developers with pull requests they can simply review and merge.
Why You Can't Build This Internally Anymore
If you've worked in a high-functioning security org, you've already seen pieces of this automation. You've seen the Python scripts that re-rank findings against the service ownership graph. You know about the detection-as-code repository that nobody outside the team knows exists. You've seen the runbook that is secretly a state machine.
These internal projects are the connective tissue that turns generic tools into a system that fits a specific business, but the workload is growing faster than any team can hand-roll glue code. Maintaining custom scripts to normalize data from five different security tools is not a scalable strategy, and as code volume multiplies due to AI developer tools, internal triage scripts will break faster than anyone can patch them. This is precisely why smart teams have stopped trying to fix their scanner stack piece by piece and started building around it with purpose-built security harnesses instead.
Key Capabilities to Require During Evaluation
When you evaluate automated SAST triage platforms, you must look past marketing claims and test specific technical capabilities. The tool must integrate seamlessly into your developer environment and provide undeniable proof of its accuracy.
Contextual Reachability Analysis
Finding a vulnerable open-source library in a repository is useless if the application never calls the vulnerable function. Your triage tool must perform reachability analysis, evaluating the call graph to determine if external inputs can actually reach the vulnerable code path. Tools lacking this capability will continue to surface theoretical risks that have zero practical impact on your security posture.
AI and LLM-Driven Validation
Rules-based filtering is no longer sufficient. Modern platforms utilize large language models trained specifically on secure coding practices and vulnerability patterns. This AI layer analyzes the code snippet in question to understand the developer's intent, and it can recognize custom sanitization functions that traditional scanners miss. Evaluate the platform's ability to minimize false positives using these advanced models without introducing new false negatives.
Developer-Native Workflows
Security tools fail when they force developers to leave their primary workspace. The triage solution must integrate directly into the source code management system and deliver feedback as comments on pull requests or merge requests. If a developer has to log into a separate security dashboard to view their vulnerabilities, adoption rates will plummet. The feedback loop must be immediate and embedded in the existing continuous integration pipeline.
Automated Remediation Generation
The ultimate goal of triage is to fix the code. The most advanced automated SAST triage tools do not stop at verifying the alert, they generate the actual code patch required to resolve the issue. When evaluating this feature, test the quality of the generated code specifically: patches must match the styling conventions of the repository and must not break existing functionality. The platform should ideally open a pull request with the fix automatically.
Custom Detections Over Generic Rules
You cannot rely on generic rules to catch novel threats. A novel attack technique can land on Monday and require a control by Thursday, and no legacy scanner can adapt on that timeline. You need a tool that allows you to write, test, and deploy custom detection rules in minutes, mapped directly to your own threat model rather than a vendor's generalized one.
Integrating Triage into Your Existing Stack
A triage platform does not replace your scanners. It acts as an intelligence layer sitting between your discovery tools and your developers, which is why deep integration capabilities are a strict requirement, not a nice-to-have.
Your evaluation should verify out-of-the-box support for your specific SAST vendors, whether that's OpenGrep, Semgrep, or a legacy scanner. The platform must be able to ingest native report formats without custom scripting, and it must integrate securely with your issue tracking system. When a vulnerability is verified, the tool should automatically create a Jira ticket with all the necessary context, code snippets, and remediation guidance, and when the vulnerability is fixed and merged, the tool must automatically close the ticket. Bidirectional synchronization is critical to maintaining a single source of truth for your security posture.
Measuring the ROI of Triage Automation
Securing budget for a new security tool requires a clear demonstration of return on investment. The ROI for automated triage is calculated primarily through engineering hours saved and the reduction of your mean time to remediation.
You can quantify the manual triage cost by multiplying the number of alerts generated per month by the average time spent verifying a single alert, then multiplying that by the hourly rate of your security engineers. Automated platforms typically eliminate the vast majority of this manual effort.
Consider the formal calculation for Mean Time to Remediation reduction:
MTTRnew=∑(Time of Remediation−Time of Automated Verification)Total Vulnerabilities Fixed\text{MTTR}_{\text{new}} = \frac{\sum (\text{Time of Remediation} - \text{Time of Automated Verification})}{\text{Total Vulnerabilities Fixed}}MTTRnew=Total Vulnerabilities Fixed∑(Time of Remediation−Time of Automated Verification)
By reducing the time it takes to verify an alert to near zero and providing automated fixes, organizations often see their MTTR drop from months to days. This reduction fundamentally lowers the risk profile of the organization while simultaneously increasing developer productivity. Beyond the direct time savings, automated triage also reclaims your most expensive talent: security engineers are hard to hire, and having them manually click through false positives is a poor use of that scarcity. Automating triage frees your best people to focus on threat modeling, architecture reviews, and complex incident response instead.
Frequently Asked Questions
What is the difference between an AI scanner and an agentic security harness? An AI scanner looks for vulnerabilities in code. An agentic security harness orchestrates the entire workflow: it contextualizes the alert, verifies reachability, prioritizes based on business logic, and deploys automated fixes.
Can automated triage tools work with my existing SAST scanners? Yes. Modern triage tools are designed to sit on top of your existing scanner stack. They ingest alerts from your current tools and apply context-layer filtering to separate the signal from the noise, rather than requiring you to rip and replace anything.
How does reachability analysis reduce false positives? Reachability analysis maps the execution paths of your application. If a SAST scanner flags a vulnerable function, but that function is never called or exposed to user input in your deployment, the triage tool flags it as unreachable and reduces the priority of the alert accordingly.
Why are custom detections important? Generic scanners optimize for average risks across an average customer base. Custom detections let you write rules specific to your own architecture and business logic, so you can enforce the security requirements that are unique to how your organization actually operates.
Making the Final Decision
Buying automated SAST triage tools requires a shift in how you view application security. You are moving away from metrics based purely on discovery and moving toward metrics based on resolution.
When conducting your proof of concept, define clear success criteria. Measure the exact reduction in false positives. Track how many automated pull requests are successfully merged by the development team. Evaluate the platform's accuracy against your most complex, legacy repositories. The right tool will demonstrate immediate value by quieting the noise and allowing your security team to focus on architectural threat modeling rather than chasing down irrelevant alerts.
Stop settling for security solutions that create more work. Demand a platform that actually solves the problem it uncovers.
Ready to upgrade your AppSec operations? Apply for early access to Amplify Console and see how an agentic security harness can transform your vulnerability management today.
Subscribe to Amplify Weekly Blog Roundup
Subscribe Here!
See What Experts Are Saying
BOOK A DEMO
Jeremiah Grossman
Founder | Investor | Advisor
Saeed Abu-Nimeh
CEO and Founder @ SecLytics
Kathy Wang
CISO | Investor | Advisor

Alex Lanstein
Chief Evangelist @ StrikeReadyFrequently
Asked Questions
What is vulnerability management, and why is it important?
Why is vulnerability management important?
What makes vulnerability management extremely challenging in today’s high-growth environment?
How can Amplify help me with vulnerability management?
What technology does the Amplify platform integrate with?
Have a
Questions?
Contact Us
Ready to
Get started?
Book A GUIDED DEMO
